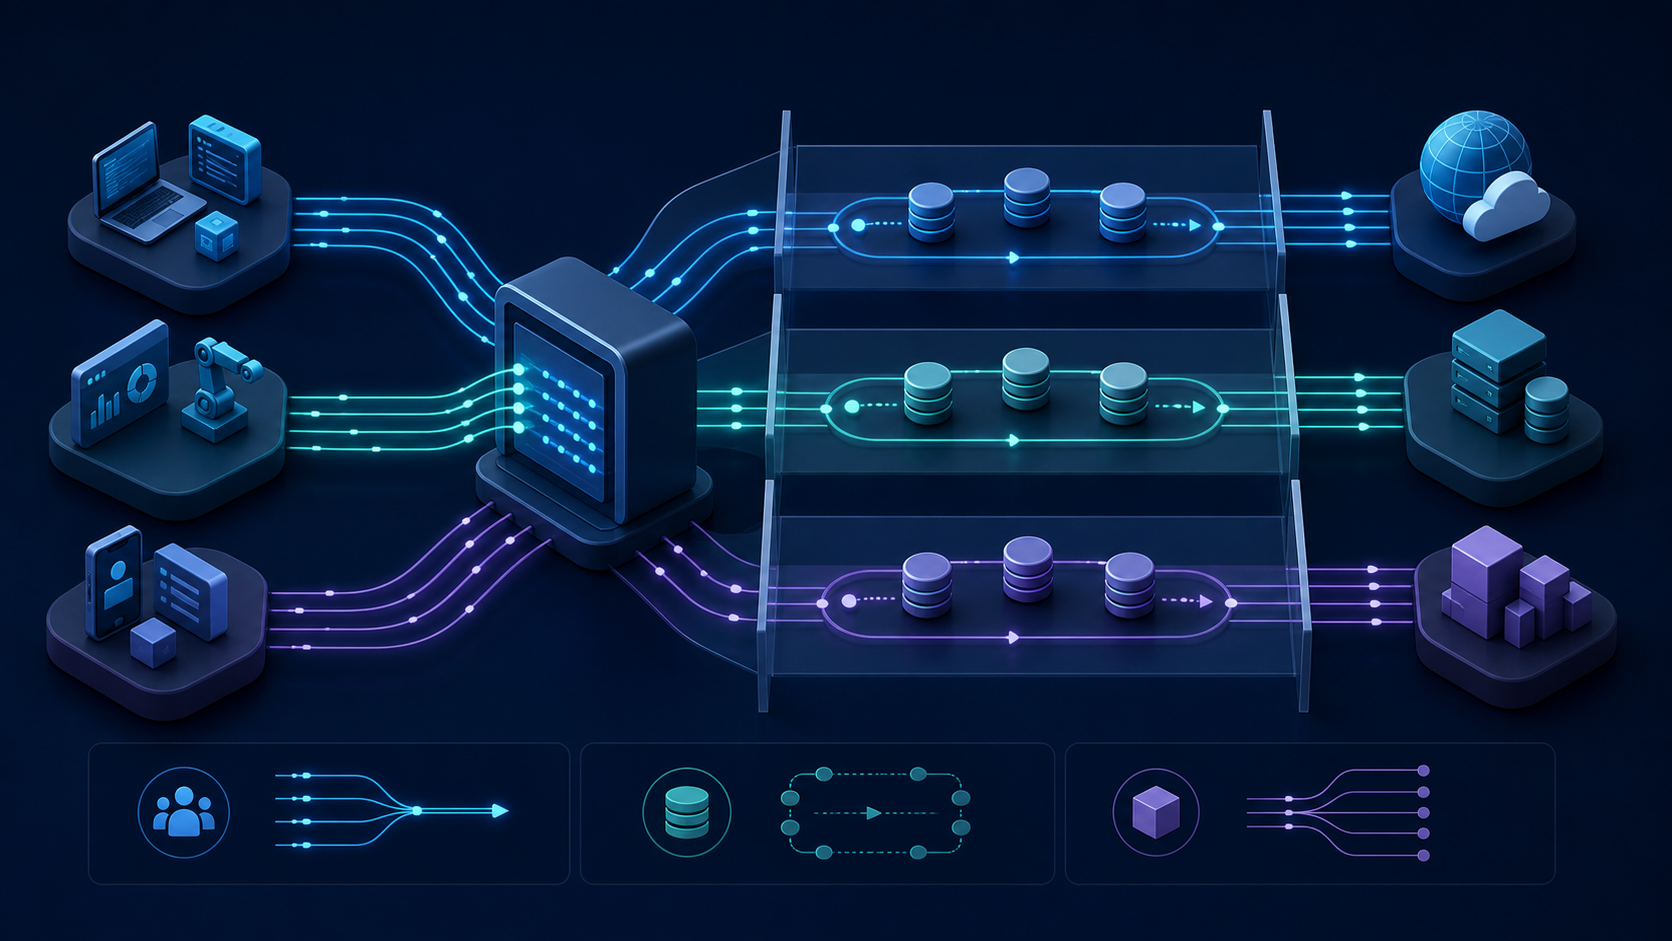
Opening a new proxy connection for every request adds DNS, TCP, TLS, and authentication overhead. Reusing healthy connections can reduce latency and resource consumption, but an incorrectly shared pool can mix credentials, sessions, regions, or workload policies. The design goal is controlled reuse inside a well-defined boundary.
What connection reuse saves
A reusable connection can avoid repeated setup round trips and reduce socket churn. Benefits are largest for short requests to the same proxy and destination, especially when TLS negotiation is involved. Measure total latency, connection time, handshake time, socket count, and reuse rate rather than assuming a larger pool is always faster.
Define the pool key
A connection should be reusable only when the security and routing context match. A practical pool key may include proxy endpoint, proxy protocol, credential or subaccount, destination authority, TLS settings, session policy, region, and network namespace.
Do not share one pool across unrelated customers, production and staging, rotating and sticky sessions, or credentials with different permissions. If a library hides its pool key, review its documentation and run controlled tests before enabling broad reuse.
Keep session semantics explicit
Connection reuse and proxy session persistence are not the same thing. A sticky proxy session may retain an exit identity across multiple connections, while one reused connection may preserve transport state without guaranteeing the same application session.
Record the intended session identifier separately from the socket. When rotation is required, confirm that connection reuse does not keep an old route alive beyond the rotation boundary.
Control connection age
Long-lived connections can become stale after proxy maintenance, credential rotation, DNS changes, or network migration. Set limits for maximum idle time, maximum connection age, and pool size. Evict connections after protocol errors, authentication failures, incomplete responses, or a known network change.
Use keep-alive probes only when they match the runtime and network environment. A connection that is open is not necessarily healthy.
Handle credentials safely
Keep credentials in a secret manager and never include them in pool logs. After rotation, prevent new requests from using old credentials, drain or close affected connections, then verify that every worker uses the new secret.
Credential identity may be part of the pool boundary even when two accounts reach the same proxy hostname. Older client versions can contain connection-reuse defects, so maintain supported versions and review official security advisories.
Size pools from real concurrency
Pool size should follow measured concurrent demand, destination limits, and proxy capacity. An oversized pool wastes sockets and can amplify bursts; an undersized pool creates queue delay. Track active, idle, queued, created, reused, evicted, and failed connections.
Use per-destination and global concurrency controls. Pooling reduces setup cost; it does not authorize unlimited parallelism.
Validation workflow
- Establish a fresh-connection baseline.
- Enable reuse for one workload and one credential.
- Compare latency percentiles, success rate, and socket count.
- Rotate credentials and verify old connections are retired.
- Change region or session policy and confirm a new pool boundary.
- Simulate stale sockets, proxy restarts, and partial responses.
- Confirm logs contain no credentials or authorization headers.
Common failure patterns
- Requests use the wrong region after a configuration change.
- Rotated credentials appear ineffective because old connections remain alive.
- One tenant experiences another tenant's session behavior.
- Stale idle connections fail the first request after a quiet period.
- Layered pools in the SDK, HTTP client, and service mesh multiply sockets.
- Retries create more connections than the concurrency limit expects.
Production checklist
- Pool keys include all security and routing dimensions.
- Tenants, credentials, environments, and session modes are isolated.
- Idle time, lifetime, and maximum pool size are bounded.
- Network and credential changes trigger safe eviction.
- Reuse and fresh-connection metrics are compared.
- Library and queue concurrency do not multiply unexpectedly.
- Client versions and official security advisories are reviewed.
- Logs are useful but credential-free.
- Proxy use follows applicable laws, destination terms, and data policies.
For controlled proxy configurations across regions and workloads, review the available service information on 98IP. Reuse connections for measured performance, but isolate every security and session boundary.
Research basis: libcurl connection reuse and fresh-connection documentation; curl persistent connection guidance; HTTP client connection-pool practices. Source names are listed without external links.
Related Recommendations
- How to Switch Proxy Providers Without Breaking Production
- Diagnose Truncated Web-Scraping Responses Before Blaming the Proxy
- Apple mobile phone set up static IP tutorial, what is the role of long-term IP agents?
- How to set up the Firefox proxy server? Just these few steps are easy to get done
- Proxy 429 Rate-Limit Handling: Respectful Recovery Without Wasting Requests
- Python Rotating Proxy Guide: Sessions, Retries and Troubleshooting
- Solve the IP restriction problem and no longer worry about "blocking access"!
- How to set a computer to access the Internet with static IP? Here are the detailed steps
- How to Test Proxy Keep-Alive Without Breaking IP Rotation
- How to Validate a Proxy SLA Before You Buy