
Your proxy extraction call returns HTTP 200, but the worker receives no usable endpoints. Before assuming that the residential pool is empty, identify where the result disappeared: the response may contain an application error, the documented list may genuinely be empty, or your parser may have discarded valid entries.
This guide is for authorized integrations using the proxy extraction mode available to their account. It describes a diagnostic workflow, not a claim that extraction calls or quota-consuming tests have been executed here. Obtaining an endpoint and successfully connecting through it are separate acceptance stages.
1. Name the empty state precisely
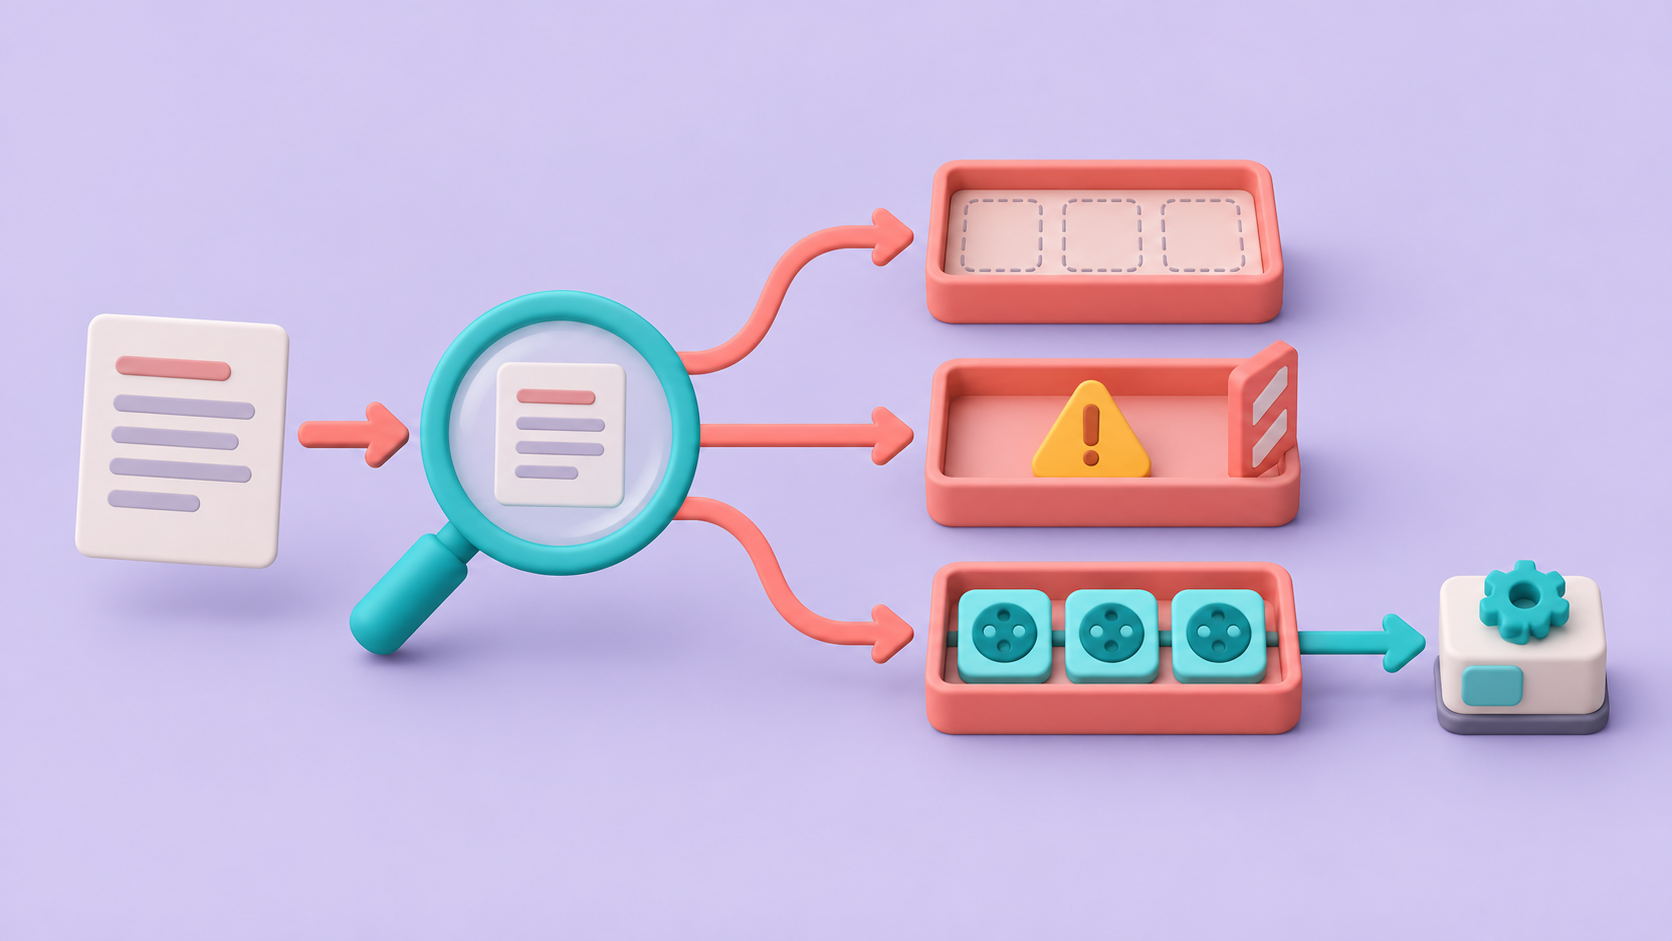
- No usable response: timeout, transport failure, or missing or incomplete content that the contract does not define as a valid empty result. Record it as a request or response problem, not a confirmed empty pool.
- Application error: the response reports a failure under the API's documented contract, regardless of the HTTP status.
- Confirmed empty result: the documented successful response contains the expected list or text format with zero entries.
- Local empty output: the captured response contains entries, but selection, decoding, parsing, validation, or filtering produces none.
HTTP 200 describes HTTP-level success; your integration must still interpret the response representation and the API's business contract. Never convert every exception into an empty list. That erases the evidence needed to distinguish these four cases.
2. Freeze one failing request safely
Record the request time with timezone, method, endpoint path, selected product or mode, requested count, approved geographic filters, output format, client version, HTTP status, media type, and response size. Capture the application status and safe error text if the documented format supplies them. Retain a restricted response sample only when it is permitted and necessary.
Use the 98IP public API configuration documentation for the actual contract. It identifies appKey as a required common parameter. Keep that value in approved secret storage; do not paste a generated URL containing it into logs, screenshots, tickets, or browser history for convenience. An extraction key is not automatically the same credential used to authenticate a later proxy connection.
Check the current method-specific documentation and the generator available in your authenticated account. This article deliberately does not invent endpoint methods, result-field names, error codes, stock levels, or account limits that have not been verified.
3. Verify the response before counting endpoints
- Check whether the request reached the intended API host and path. Record redirects and the final media type; a login HTML document is not an endpoint list merely because the client followed a redirect successfully.
- Read the documented application outcome before selecting entries. Treat authentication, permission, parameter, balance, quota, and rate-limit messages according to their actual documented meaning; do not classify an unknown response as inventory exhaustion.
- Confirm that the configured output format matches the parser. A text endpoint list, JSON wrapper, and another supported representation require their own handling. Distinguish a missing list field, a null value, malformed data, and a valid zero-entry list.
- If content appears truncated or invalid, preserve the safe response evidence and fail parsing explicitly. Do not silently pass partial data onward or invent a success result.
Compare the selected product and authentication mode with the 98IP dynamic residential proxy page. Its API, username/password, and allowlist extraction entry points describe different configuration choices. Confirm what your account and current documentation actually support; the product page does not guarantee that any requested filter always has available endpoints.
4. Isolate parameters without changing the job's authorization
- After confirming credentials and permissions, generate one baseline request using the authenticated configuration tool or documented method. Use the smallest count allowed by that method and the same approved product and scope.
- Compare it with the failing request field by field, excluding secret values from shared evidence. Check spelling, encoding, value types, selected output format, and unintended stale parameters.
- Change one supported filter at a time. Broaden a region or remove an optional constraint only if the diagnostic scope and intended job permit it. A result from another country does not satisfy the original country's requirement.
- Record each outcome as error, confirmed empty, or populated. Stop when the evidence identifies a configuration difference or when the authorized attempt budget is reached.
A broader approved query returning entries while the narrower query is empty supports a filter-specific investigation. It does not prove permanent shortage, and it does not authorize silently substituting the broader results into production.
5. Count each transformation in the local pipeline
For a captured permitted response or a synthetic fixture, record four counts: entries present in the documented payload, entries parsed, entries accepted after endpoint-format validation, and entries retained after your own deduplication or business filters. Keep safe rejection categories beside the counts. Use a single run ID so logs from different calls are not accidentally compared.
If the payload has five entries and parsing yields zero, investigate the format or selector before contacting the pool operator. If parsing yields five but validation retains zero, inspect the expected hostname or address and port representation against the actual contract. If your own filters remove all five, that is a local selection outcome. These are illustrative counts, not measured provider results.
Do not assume every colon separates a host from a port: supported representations can require more careful handling, especially with IPv6. Do not fetch fresh endpoints repeatedly merely to test the parser; replay permitted redacted fixtures or synthetic data without exposing secrets.
6. Keep extraction, freshness, and connectivity separate
Once entries exist, use one still-valid endpoint for a minimal authorized connection test, with the required protocol and runtime authentication. Record extraction time and the lifetime specified for that resource. An expired endpoint or a later 407-style proxy authentication error is not evidence that the earlier extraction response was empty. Error formats vary by protocol, so use the actual client result.
Do not repeatedly extract to fix a target website's authorization failure. Likewise, do not reuse an old saved endpoint without checking its validity to make the extraction stage appear healthy. The evidence should say which stage passed and which remains unresolved.
7. Stop unproductive retry loops
For an explicit configuration or authentication error, correct that condition before another call. For a confirmed empty response, apply the provider's documented retry guidance and your own bounded attempt and time budget. For an unknown outcome, preserve the response and investigate rather than labeling it successful or empty. Check whether extraction calls consume quota or incur other account effects before testing.
A useful support packet contains the redacted method and parameters, timezone-aware times, safe response outcome, requested versus returned counts, and the smallest reproducible authorized case. Include a provider request identifier if available. Never include appKey, proxy passwords, signed URLs, or unrestricted endpoint exports.
FAQ and a validation checklist
Does an empty result prove that the entire provider pool has no IPs? No. It describes the observed request under its parameters and account context, after the response has been correctly interpreted.
Should the parser return an empty list on every failure? No. Preserve distinct error, invalid-format, empty, and populated states so the next action matches the evidence.
- The method, product, permissions, parameters, and output format match current documentation.
- HTTP outcome, application outcome, and payload structure are recorded separately.
- Payload, parsed, validated, and retained counts identify where entries disappear.
- Controlled parameter changes stay within the approved job scope.
- Connection checks use valid endpoints and remain separate from extraction results.
Rehearse locally with a valid populated fixture, a documented empty shape, an application-error fixture, and a malformed or wrong-format fixture. Confirm that each reaches a distinct diagnostic state. These exercises are proposed checks, not executed test results. Use only authorized accounts and targets, respect request limits, and retain data and secrets under your organization's policies.
Related Recommendations
- HTTP 200 Is Not Enough: Validate Regional Ad Landing Pages Before Launch
- Browser Proxy Bandwidth Budgeting: Measure Cost Before You Scale
- How to Test NO_PROXY Rules Before Traffic Bypasses Your Proxy
- Proxy Embedded Login Failures: Compare the Top-Level and iframe Session
- How to Test Localized Checkout with Residential Proxies
- How to Audit ASN and Prefix Concentration Before Buying a Proxy Pool
- Python Rotating Proxy Guide: Sessions, Retries and Troubleshooting
- How to Compare Proxy Plans by Cost per Successful Request
- How to Normalize IPv4-Mapped IPv6 Addresses in Proxy Logs
- How to verify the location accuracy of residential agents before expanding traffic