
A browser using a regional proxy reaches a success page, but the application's background job remains pending. Changing the browser IP may leave the real problem untouched: the provider's webhook is a separate server-to-server request. Test the browser journey, event delivery, receiver acceptance, and business result as four distinct checkpoints.
This procedure is for an owned staging application and an authorized provider sandbox or mock service. It describes tests to perform, not results already measured on 98IP. Use a harmless synthetic job, with no real purchase, message, or production account change.
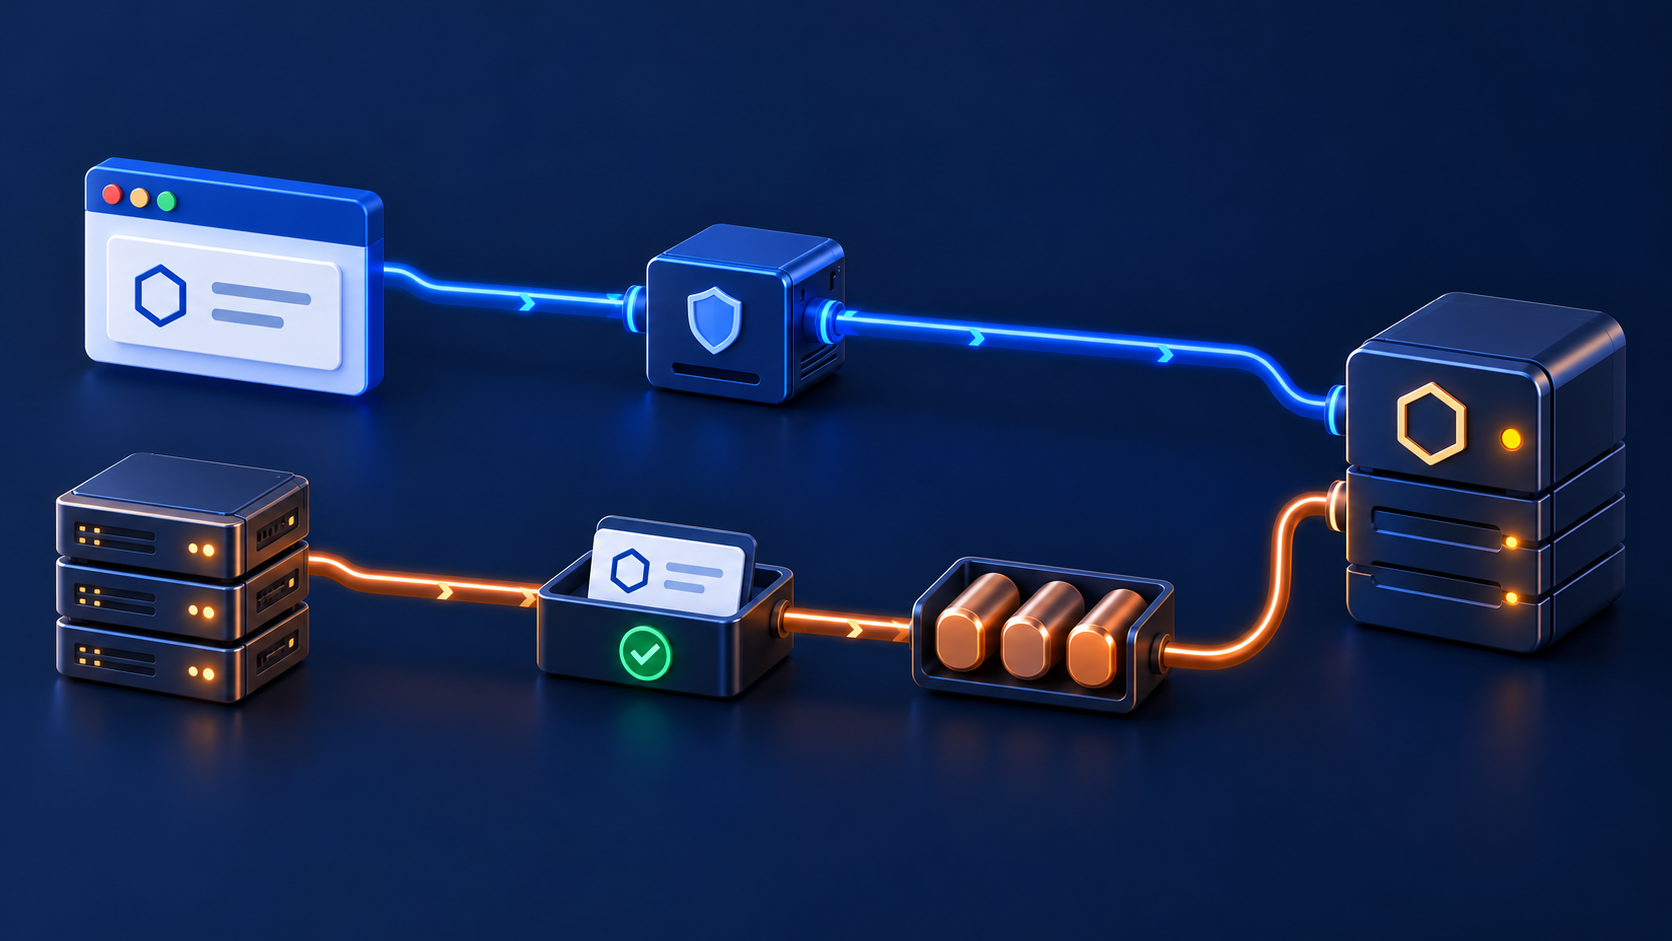
1. Draw the two paths before testing
The first path is browser → configured proxy → application or provider page. A return page, redirect, or browser polling request belongs to this user-facing journey. The second path is provider server → registered webhook receiver → queue or handler → stored application state. Unless your architecture explicitly routes it otherwise, configuring a browser proxy does not route an incoming webhook through that proxy or create a public callback endpoint.
Record the actual receiver hostname, sandbox environment, subscribed event types, and processing component. Identify any reverse proxy, ingress, or gateway in front of the receiver separately. A sender-side allowlist should follow that provider's documented policy; the browser exit address is not proof of the webhook sender's identity.
2. Agree on a four-stage evidence record
For each run, retain a safe test run ID, synthetic job ID, provider event ID where available, environment, event type, browser region, and timestamps with a timezone. Define the observation deadline from the application's agreed service target and the provider's documented delivery behavior; there is no universal callback timeout to copy into every system.
- Browser: which authorized job was initiated, and what return page or status was shown?
- Sender: was the expected event created, and which endpoint and delivery attempt did the provider report?
- Receiver: did the edge and application receive it, authenticate it, and durably accept it for processing?
- Business result: did the handler complete the expected state transition for that exact job, without a second side effect?
Keep raw payloads and signing material in restricted test tooling. Shared evidence should contain identifiers, redacted errors, and processing outcomes, not session cookies, signatures, secrets, or customer data. Delivery IDs and business object IDs may differ; document the mapping instead of assuming one identifier describes every stage.
3. Hold the receiver fixed while changing browser routes
- In the approved sandbox, register the owned receiver and verify that its environment and event subscriptions match the test. Use the provider's test-event facility to establish receiver reachability first. A generic sample event proves only that sample path, not the full browser-created job.
- Run one baseline browser journey with fixed account permissions, locale, application build, and receiver configuration. Create one synthetic job and capture its correlation IDs.
- Repeat through one selected residential proxy region with a new equivalent job. Change only the browser route. Keep the receiver, handler deployment, and event configuration fixed, and check all four stages again.
- Compare the two evidence records after each reaches the agreed terminal state or observation deadline. Do not infer receiver health from the browser screenshot.
For a controlled regional browser path, review the 98IP residential proxy options and confirm the actual region and session configuration before the run. The website testing use case explains the relevant application context. These products support the route comparison; they do not supply or certify your webhook receiver, provider sandbox, signature implementation, or end-to-end delivery latency.
4. Separate delivery acknowledgement from completed work
Check the actual provider's signature scheme and SDK instructions. For example, Stripe signature verification depends on the unmodified request body. Do not disable validation to make a proxy test pass. Confirm that accepted events are recorded or durably queued according to your architecture before treating the acknowledgement as a successful handoff.
An HTTP acknowledgement and application completion are different observations. HTTP 202 means a request was accepted for processing, not that processing has finished. Even a receiver returning 200 can have a failed worker downstream. Record both the delivery response and the handler's final state, including a safe error category when processing fails.
5. Use controlled failures to locate the boundary
Perform the following only in the isolated test environment. Restore the changed component after each case and repeat the healthy baseline. These are proposed exercises, not claims of tests executed here.
- Close the test browser after initiation: the independently generated webhook should still be evaluated by the receiver. If the job design actually depends on a later browser action, document that dependency rather than assuming a webhook was due.
- Pause only the test worker: observe whether authenticated delivery is durably accepted while the business result stays pending. Restore the worker and verify the exact job finishes. Do not acknowledge work that will be lost when the process exits.
- Use an intentionally invalid signature in the provider-supported test mechanism or owned mock: the receiver must reject it without a business state change. Do not put the real signing secret in a browser script.
- Redeliver the same sandbox event through the provider's supported facility: check that delivery attempts remain visible but the business effect is not repeated. Use provider-specific event identity and ordering rules; not every sender has the same retry policy.
6. Interpret missing evidence without blaming the IP
No sender event may mean the prerequisite job or subscribed event never existed. Sender delivery failure points toward receiver reachability, TLS, endpoint selection, or the provider's delivery rules. Edge receipt followed by authentication failure calls for environment and signature checks. Accepted delivery with no state transition calls for queue, handler, and object-mapping investigation. A completed job with an outdated page calls for the browser's status refresh path.
These are investigation branches, not automatic root-cause verdicts. A browser route can change whether the initiating operation succeeds, while the callback still follows another route. Correlate the actual job and event before drawing conclusions; do not create new jobs merely to make a missing callback disappear.
FAQ and acceptance checklist
Does a successful return page prove a webhook arrived? No. Require sender, receiver, and business-state evidence for the correlated job.
Will a sticky browser session keep the callback IP fixed? Browser session settings do not establish the sender's server egress. Inspect the separate callback architecture.
- Browser and server paths, environment, event subscriptions, and endpoint ownership are recorded.
- Each run maps the synthetic job to its sender event, receiver decision, and final state.
- Observation deadlines and provider-specific retry rules are explicit.
- Invalid signatures cause no state change; repeat delivery causes no repeat business effect.
- The restored healthy scenario passes on both baseline and selected browser routes.
Use authorized sandbox accounts, synthetic data, and approved endpoints. Respect rate limits and provider test-event rules. Avoid production side effects, never open an unapproved public listener for convenience, and remove test payloads under your retention policy.
Related Recommendations
- Proxy Bandwidth Cost Estimation: Budget by Useful Results, Not Price per GB
- How to Test TLS Certificate Revocation Through a Proxy
- WebSocket Proxy Compatibility Test: Handshake, Heartbeat and Recovery
- Proxy Pool Quarantine and Recovery: Stop Unhealthy Exits From Returning Too Soon
- Regional Proxy CSV Export Checks: Validate Records Before Opening the Spreadsheet
- Do Two Proxy Providers Share the Same Exit Pool? An Overlap Test
- Proxy 304 Responses: Reuse the Right Local Copy, Not an Empty Body
- SOCKS5 Remote DNS Resolution Test: Verify the Full Proxy Path
- Sticky vs Rotating Proxy Sessions: A Practical Selection and Testing Guide
- Proxy Geo-Targeting Accuracy Audit: Test Country, Region, City and ASN Claims