
A script returns HTTP200 during an authorized regional browser test, yet the page never reaches its expected ready state. The console reports an integrity mismatch. Download success and permission to execute are separate observations. Before replacing the proxy exit, establish which released bytes the HTML expected and which bytes the browser actually received. This guide describes a controlled test design; it does not claim a measured 98IP result.
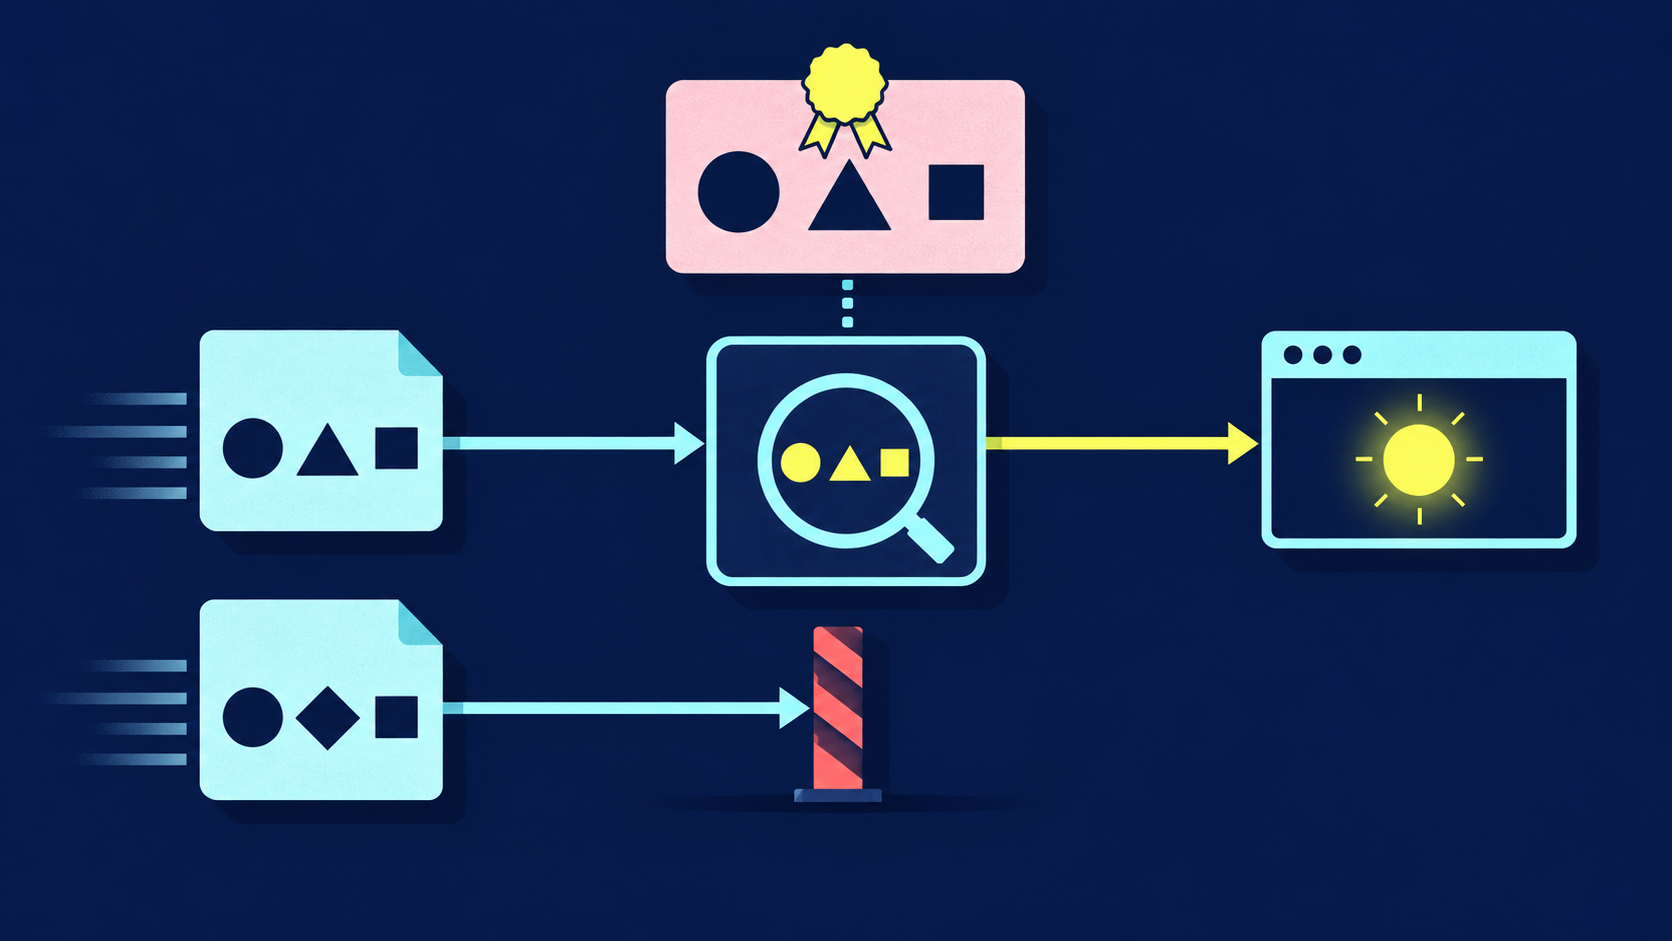
1. Confirm that the failure is really SRI
Subresource Integrity, or SRI, lets a page supply a cryptographic digest for a script or stylesheet through its integrity attribute. A fetched resource that fails the applicable integrity check cannot be used as that resource. HTTP200 only establishes the HTTP response status; it does not establish successful integrity verification or script execution.
Record the actual script element's resolved src, integrity value and crossorigin setting, the final response URL, status, content type and the relevant browser console message. Preserve the deployed HTML version and asset release identifier. Redact tokens and query secrets. A wrapper's generic “proxy script error” is not enough to identify the browser check that failed.
Separate integrity mismatch from CSP rejection, CORS failure, incorrect JavaScript MIME type, network failure and an exception after execution begins. They can all leave a page marker absent. If the console names a policy failure instead, investigate that policy with the owner; the CSP resource diagnosis guide addresses that different boundary.
2. Compare the correct bytes against an independent release
Use the owner's reviewed final build artifact as the expected input, after approved minification and other build transformations. For a simple controlled fixture, use one SHA384 integrity entry generated by the release process. The digest is Base64 output with its algorithm prefix, not a hexadecimal checksum pasted behind that prefix. Do not invent a sample digest or treat its length alone as proof of correctness.
Compare the expected artifact with the received representation after HTTP content codings have been decoded. A gzip or Brotli wire file is not the same input as the decoded script bytes. Do not normalize line endings, re-save text in another encoding, prettify the source or hash text copied from a developer-tools viewer. Such operations can change the bytes being diagnosed. If the capture tool cannot preserve the relevant decoded bytes, state that limitation instead of asserting a match.
Compute an expected digest from the independently approved artifact and a diagnostic digest from the observed decoded response. Keep their provenance separate. Copying a new hash from an untrusted response into HTML merely makes that response the new expectation; it does not establish that the response is the intended release.
3. Test a valid, changed and corrected fixture
- Use an owned HTTPS staging page and a harmless script that sets a fresh, uniquely identifiable test marker. No real advertising, analytics, checkout or customer data should be triggered. Agree on the marker and release identifier before running the test.
- Create the positive fixture: the final approved script and its matching integrity metadata. Start with a same-origin asset to isolate integrity from cross-origin configuration. Ensure the page's CSP permits the fixture and the script MIME type is appropriate.
- Create the negative fixture by changing one harmless comment byte in a separate owned copy while retaining the positive fixture's old hash. The expected result is an integrity rejection and no new execution marker. Keep all other settings equivalent.
- Create the corrected fixture as an owner-reviewed new release whose asset and HTML integrity metadata are paired. It should produce its own expected marker. The changed-copy negative fixture must still fail.
- Run the three cases through the approved baseline and selected residential route, using equivalent initial browser state. Record real egress and keep the route's session policy stable while comparing cases.
- Correlate console evidence, final asset bytes, HTML metadata and the fresh marker. Clear or version the marker between cases so an old successful run cannot make a blocked script look executed.
These are expected outcomes, not published measurements. If an authorized baseline is unavailable, record that explicitly. A deliberately modified fixture proves that the test can detect a mismatch; it does not prove a regional CDN or proxy modified a production file.
4. Find the first release or delivery divergence
- Old HTML references new bytes at a mutable asset URL: inspect deployment ordering, cached HTML and CDN asset replacement. Restore the owner's matching release pair, preferably through its versioned immutable asset process.
- HTML has the intended release but the observed bytes differ: compare final URLs, redirects, CDN deployment versions and any approved edge transformation with the release owner.
- Decoded bytes match the approved artifact but verification still fails: check the exact integrity metadata, algorithm/output format, resource eligibility and browser-reported CORS conditions. Do not infer success from a hand-edited string.
- Only one region differs: preserve the region's HTML and asset versions, cache evidence and deployment identifiers before attributing the fault to an exit address.
- The script passes integrity but the page is broken: investigate script runtime and application readiness separately. Passing SRI does not certify the script's business behavior or safety.
Browser cache, service workers and CDN caches can supply different release combinations. Record how each test response was obtained and reproduce with equivalent initial state. Do not add arbitrary cache-busting parameters that may alter routing or content without documenting that change. An ordinary non-intercepting HTTPS proxy cannot edit the encrypted target script; authorized TLS inspection introduces a separate trust boundary that must be recorded.
5. Handle cross-origin assets without weakening checks
For a cross-origin SRI resource, the request must satisfy CORS requirements as well as integrity. On an owner-approved public static asset, an appropriate anonymous cross-origin request and the asset server's corresponding CORS response are a common design. Review the actual request mode and response with the owner. A matching hash alone cannot repair missing cross-origin permission.
Do not blindly add wildcard credential permissions, disable certificate checks, remove integrity, turn off CSP or install an extension that bypasses browser security. Those changes destroy the intended acceptance boundary. When an approved asset changes, update its reviewed release metadata and deploy the HTML/asset pair consistently; retain the mismatch negative control after correction.
The evidence packet should contain synthetic fixture identifiers, redacted element attributes, final URLs, release IDs, decoded-byte comparison results, console classification, cache/service-worker observations and fresh execution markers. Avoid cookies, authentication headers and proxy passwords. A screenshot is supporting evidence, not a substitute for byte provenance.
6. Use 98IP for the regional comparison and close the test
When authorized website testing requires a residential route, consult the 98IP residential proxy product page and API configuration documentation, then use the access method and parameters supported by your account. Compare one controlled route at a time after fixing the page and artifact expectations.
A proxy supplies a network path; it does not repair stale release metadata or guarantee browser execution, target compatibility or a particular regional result. Limit synthetic requests, check actual account usage and respect the site's authorization. This procedure makes no performance or billing promise.
- The actual console failure is classified as SRI, CORS, CSP, MIME, network or runtime.
- Expected bytes come from a reviewed final artifact, independently of the observed response.
- Hash comparisons use decoded representation bytes without text normalization.
- Positive and corrected fixtures execute fresh markers; the changed negative fixture remains blocked.
- HTML, asset, cache, service-worker and regional release evidence are correlated.
- The repair preserves integrity and cross-origin security controls.
Can HTTP200 still accompany a blocked script? Yes. The browser can receive a successful HTTP response and then reject the resource's integrity.
Does SRI failure prove the proxy changed JavaScript? No. Release pairing, delivery versions and browser security conditions require independent evidence.
Should I replace the HTML hash with the fetched file's hash? Only an approved release process should establish the expected artifact. A hash derived solely from the suspect response cannot validate its provenance.
Related Recommendations
- How to Test Encrypted Client Hello Through a Proxy
- How to Choose and Test a Residential Proxy Rotation Interval
- Python Rotating Proxy Guide: Sessions, Retries and Troubleshooting
- How to Test Proxy IP Reputation Before Production
- HTTP425 Through a Proxy: Check Early Data Before Rotating the Exit
- How to Run a Residential Proxy Pilot That Produces a Defensible Buying Decision
- Proxy NDJSON Streams: Test Read Boundaries Before Blaming Missing Records
- Proxy Geo-Targeting Accuracy Audit: Test Country, Region, City and ASN Claims
- How to Audit HTTP/2 Server Push Cleanup in Shared libcurl Clients
- Resources Blocked Through a Proxy? Separate CSP from Network Failure