
A store locator sees the expected proxy region, yet its “use my location” action fails. These observations concern different inputs. The website's IP-derived region is not proof of a device coordinate, and denying browser location access is not itself a proxy outage.
For an authorized regional website test, accept the location journey as a state transition: the app requests a location, receives a result or failure, explains the state, and offers a usable next action. This guide proposes tests for owned staging applications; it does not claim any browser or 98IP performance result.
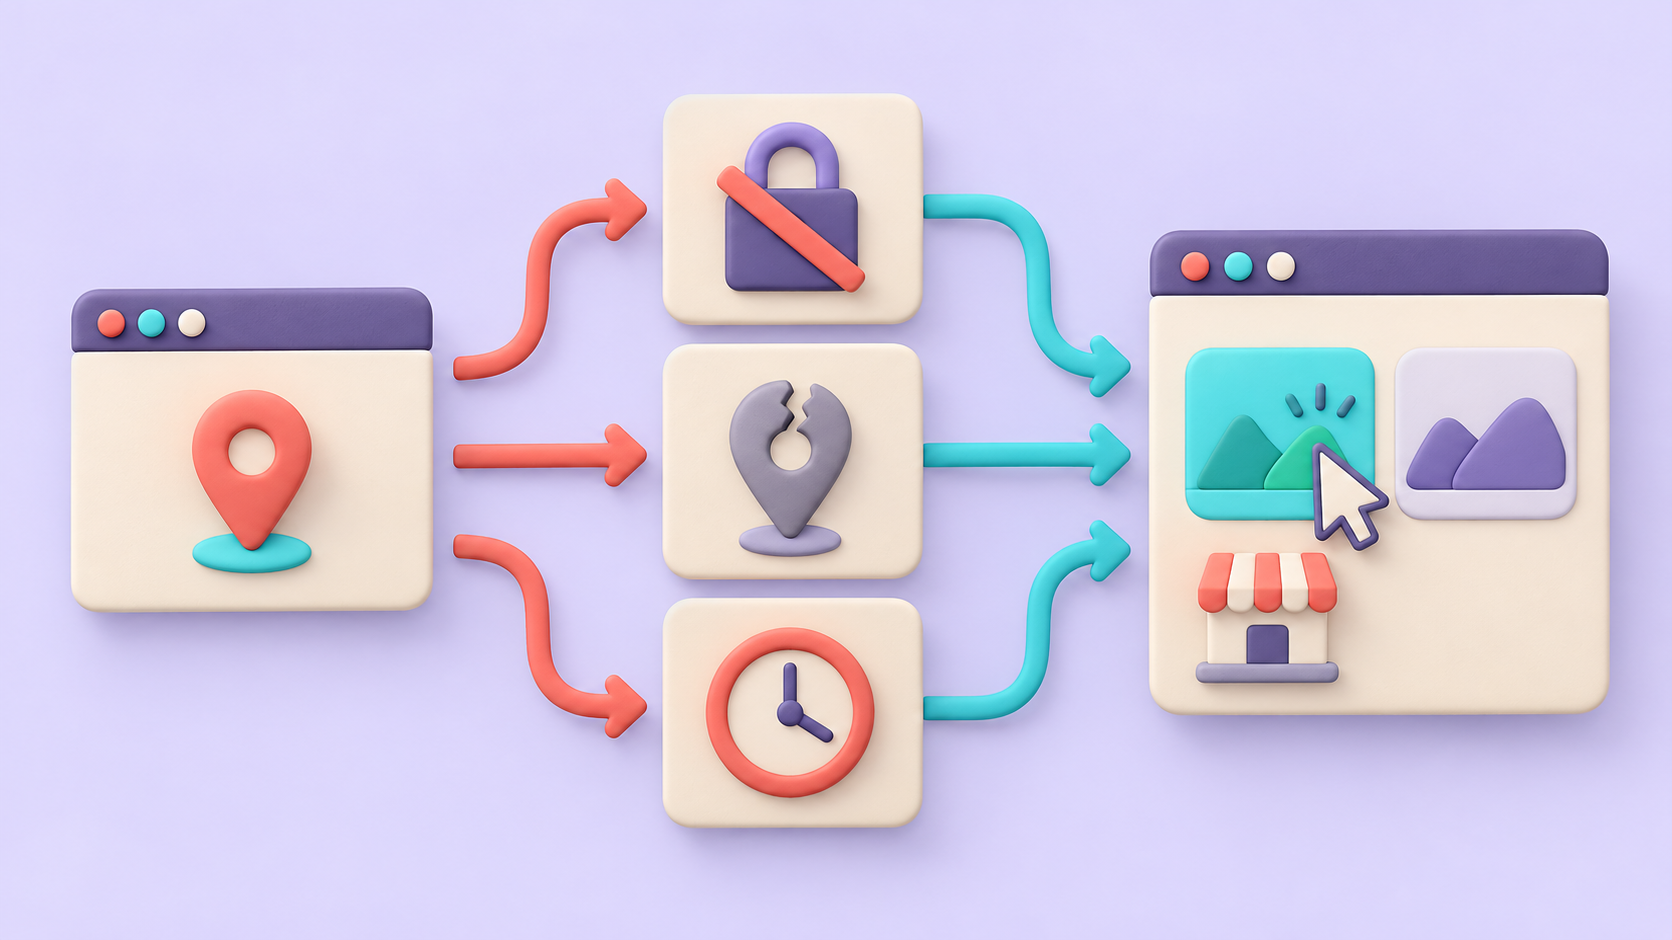
1. Separate network region from device location
Keep two evidence columns. The first records the approved proxy route and coarse regional response from your owned endpoint. The second records the browser location request, its permission context and its callback result. Do not copy an IP database's city into a field labeled device coordinates.
Use the 98IP dynamic residential IP product page when choosing the product for regional route comparisons, and confirm the actual location options in your account. That route is useful for testing an application's regional defaults. It does not guarantee the browser's Geolocation API returns coordinates for that region. Check documented connection setup through the API configuration page.
2. Write a fallback contract with the product owner
Choose a small owned fixture: a store selector with two synthetic areas and known store IDs. Define what should happen after a denied request, an unavailable result and a timeout. A reasonable product contract may keep manual area entry available, explain that automatic location did not complete, and avoid presenting a coarse default as a precise current position.
Record which source wins when the user manually chooses an area. Define what a later automatic result may change and what requires confirmation. A delayed callback must not unexpectedly replace the location the user just selected. Agree on an application waiting deadline and its visible state before testing; do not discover the acceptance threshold by watching one fast run.
3. Check prerequisites before attributing an error
Browser geolocation requires a secure context and permission, and can be restricted by Permissions-Policy. Record browser and OS versions, top-level or embedded context, site permission settings, system location settings and the owned page's relevant policy. A missing prompt is not enough to conclude that the user explicitly declined: stored settings or policy may be involved.
Record the actual request options, including timeout and maximumAge. Cached-position acceptance is separate from the current network route. Mark any development coordinate override as synthetic; it tests application handling, not physical location or real sensor acquisition.
4. Exercise three failures and one recovery
- Permission denied: use the browser's normal site controls in an isolated test profile. Trigger the owned page's location action. Capture the callback outcome and verify that the app leaves its waiting state, explains the limitation and preserves manual selection. Restore the profile setting after the case.
- Position unavailable: use a documented test seam in the owned application to deliver this error to the same handler. Label it simulated. Do not disable a real device's services merely to claim a repeatable sensor test.
- Timeout: use a controlled delayed test adapter and verify both the location error path and the application's agreed waiting deadline. A spinner must not obscure the manual control indefinitely.
- Recovery: start from the failed state, select a synthetic area manually, then deliver a late success through the owned adapter. Check the agreed source-precedence rule and retained store choice.
The browser error codes distinguish permission denied (1), position unavailable (2) and timeout (3). Preserve the code rather than classifying by translated message text. Code 1 does not, on its own, identify the exact permission-setting cause. If the API is absent or invocation fails before a callback, record that separately instead of inventing one of these codes.
5. Cross the failure cases with a route comparison
Run the small matrix on a baseline route and one approved proxy route while keeping the browser context and synthetic fixtures equivalent. Log case ID, route alias, initial permission state, simulated or native execution, callback code, elapsed time, UI outcome, selected area ID and resulting store IDs. Do not log personal coordinates or proxy secrets to prove the route.
A simulated failure validates the handler under that route; it does not prove the real location provider failed there. Keep native permission tests and adapter tests in separate result columns. If a regional default changes while manual selection and fallback remain correct, that can be an expected route effect rather than a broken permission flow.
Conversely, if the manual selector requests the wrong area's stores after a correct explicit selection, file an application-state defect. Do not repeatedly rotate exits to hide it. If a native test differs by route, reproduce with settings held constant and preserve evidence without assigning network causation prematurely.
6. Review failures at the state boundary
- Still waiting after failure: inspect whether the error handler clears the loading state and whether an app deadline has a visible outcome.
- Repeated permission pressure: verify that the user can continue manually without a prompt loop. Any retry should be a deliberate user action allowed by the normal browser controls.
- Manual choice overwritten: inspect stale callbacks and the selected-location source version.
- Coarse default presented as exact: correct the label and source metadata before treating the result as a location success.
For each defect, attach the initial state, trigger, observed transition, expected transition and owner. A screenshot alone cannot establish whether a location came from IP classification, a cached coordinate or a manual choice.
FAQ and acceptance checklist
Should rotating the proxy make the permission prompt reappear? Do not assume it will. Inspect site and browser permission state; the exit route is not a substitute for permission management.
Can simulated coordinates prove city-level proxy accuracy? No. They are fixture inputs for application behavior. Keep any separate IP-region assessment out of this permission-fallback verdict.
- Network region, device result and manual selection have distinct source labels.
- Denied, unavailable and timeout cases have explicit expected transitions.
- Manual entry remains usable and returns the known fixture stores.
- Late success respects the approved precedence rule.
- Native and simulated evidence are clearly distinguished.
The cases above are proposed exercises, not executed measurements. Use only approved targets and synthetic locations, retain normal browser protections, restore changed test settings, cap requests and remove personal location data from shared evidence. The release decision should name the tested browser/OS coverage and any untested cases rather than promise universal fallback behavior.
Related Recommendations
- How to Capacity-Plan Proxies for 200 Parallel Browser Sessions
- How to Validate Localized Prices Through Regional Proxies
- Proxy DNS TTL and Failover Validation: Prevent Stale Gateway Outages
- Can Visitors Reach Every Language URL? A Regional Proxy Audit Before Launch
- How to detect unexpected direct fallback after agent failure
- Proxy Geolocation Consensus Test: Validate Country, Region and Usability
- How to Test Proxy Header Size Limits Before Large Cookies Break Production
- How to Sanitize HAR Files Before Sharing Proxy Debug Logs
- Preventing agent retry storms: backoff, jitter, budgeting and security recovery
- How to Audit a Proxy Fair-Use Policy Before Hidden Limits Throttle Production